

Roughly $6.3 billion in digital assets drained out of Binance’s wallets across ten blockchains on Thursday, in a theft that was over in about twenty minutes. Investigators at TRM Labs and Chainalysis have both named TraderTraitor, the North Korean group the FBI holds responsible for the $1.5 billion Bybit theft in February 2025. That had been the biggest crypto theft on record. This one is four times larger.
The breach did not rely on cracking any encryption. It started with a single engineer’s laptop, which handed the attacker a way into a service container and the means to push through withdrawals that appeared genuine. Binance says no private keys were exposed. Around $3 billion has since been frozen, most of it stablecoins that Tether and Circle were able to lock. The exchange has pledged to make good on every loss and halted withdrawals while it reinforced its systems.
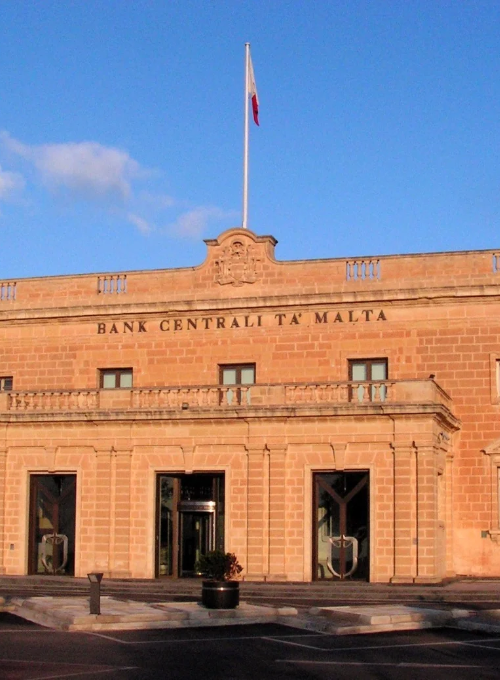
Six weeks earlier, Revolut reported a breach in which no one broke into anything. Requests for customer data came from a real government email domain, which Italian authorities later tied to the prefecture of Reggio Calabria. Staff handed over the records. Passports, transaction histories and bitcoin holdings for roughly 680 customers were given up, a group that appeared to include wealthy crypto holders. Some of those affected were in Malta. A reported $3 million ransom demand followed, which Revolut says it did not engage with.
Neither company has blamed AI. Writing in opinion, Elisa Barbieri argues the two episodes still expose how much of everyday finance sits on platforms that a single laptop or one trusting employee can bring down, and how much more fragile they get when attackers can put machines on the work.
IBM’s 2026 Cost of a Data Breach study found that one in four malicious breaches this year involved AI, up 56% on the year before. Those cases cost about $6 million apiece, roughly a million more than breaches without it. Tenable’s chief financial officer says the average time it takes to exploit a known flaw has dropped from 30 days to 1.6 days within a year.
Microsoft last week attributed a supply-chain attack on ConnectWise Cloud Backup to Storm-0940, a China-aligned group that ran an agentic hacking framework called ARTEX to automate reconnaissance and password spraying. The group attempted to log in to more than 2,250 Microsoft 365 tenants, hitting roughly 2,900 attempts a minute at its peak and in several instances secured privileged cloud access in under three hours.